
Request
Arrives with an idempotency key; retries after network errors are not processed twice.
See where every money movement began, where it waits and how it closes.
Payment, wallet and collection infrastructure built on a double-entry ledger, idempotent transaction flows and auditable state transitions.
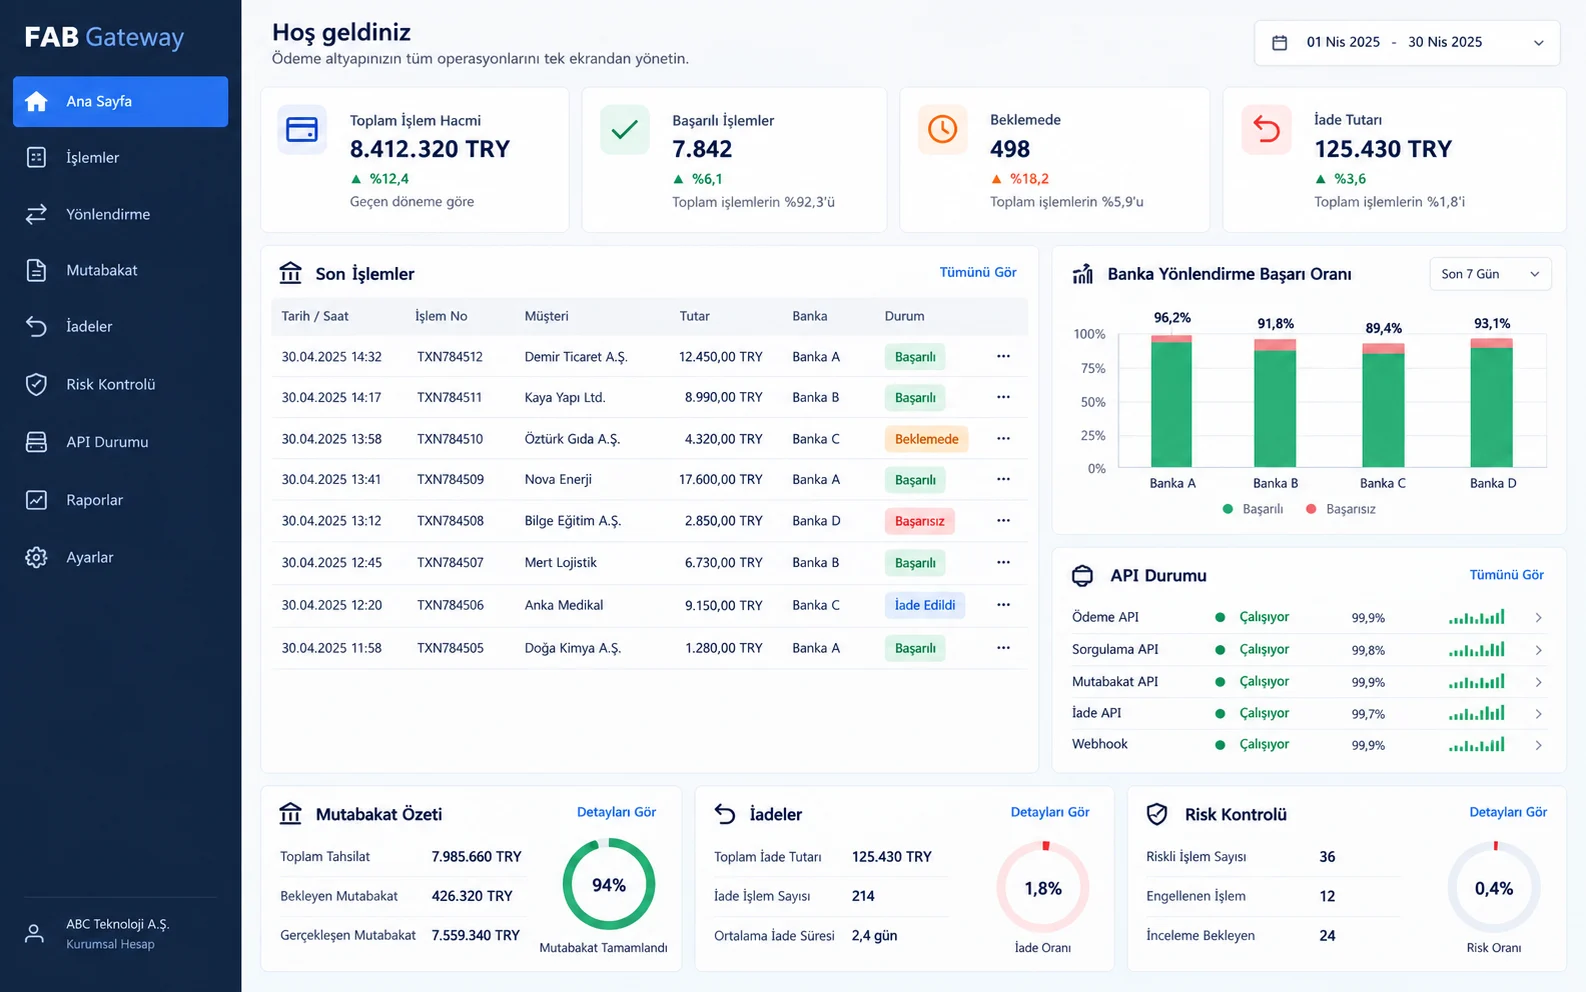
Volume, successful, pending and refunds; bank routing success and API status.
Double-entry ledger, idempotency, tokenisation and immutable audit trail.
Arrives with an idempotency key; retries after network errors are not processed twice.
Card data is replaced by a token; the sensitive zone shrinks.
Routed to the right bank; success rate tracked.
Pending, successful, failed, unanswered and cancelled as separate states.
Every movement is written as debit and credit lines.
Split into ours-only, theirs-only and amount mismatch.
Who accessed which record and when — immutably.
Pending, failed and refunded transactions.
Operations panelMismatch types and closing.
ReconciliationRisky and blocked transactions.
Risk controlAPI, webhooks and idempotency.
API statusData ownership, error handling, security and audit trails are designed as part of the implementation.
In applications that carry money the real subject is not the screen but the ledger. This platform builds payment, wallet, prepaid balance and collection processes on a double-entry ledger, idempotent transaction flows and an explicit state machine.
The most expensive faults in systems carrying financial flows are these:
Every movement of money produces at least two lines: a debit and a credit. A balance is the sum of those lines, never a separate field. That way "why is the balance this?" can always be answered from the movement list.
Every outbound call carries an idempotency key. A second request with the same key creates no new record and returns the result of the first. We cover this in the API integration guide.
Among transaction states, "no response received" is its own state and is not automatically treated as a failure. Such records are closed against the reconciliation file received from the counterparty.
Bank statements and collection channels (bank integration), virtual POS and payment institutions, e-document systems, accounting and ERP, identity verification services, and an API integration layer for enterprise applications.
On compliance scope: Card data security and financial regulation requirements depend on the nature of the business, which party holds which data, and licensing status. The compliance scope and who carries which obligation are therefore defined in writing at the start of the project. We state up front that software alone does not produce a compliance certificate.
The default design does not: the token returned by the payment provider is stored. Where card data must be held in the system, that changes both scope and responsibility, and is decided separately at the start of the project.
Not in distributed systems. The realistic target is at-least-once delivery with the receiver refusing to process the same request twice. Idempotency keys and the state machine provide that.
In three groups: present in yours but not theirs (a lost response), present in theirs but not yours (a missed notification), and present in both with different amounts (commission, rounding, currency). Each has its own resolution path; see the bank integration guide.
The ledger does not replace accounting; it produces the entries to be posted to it. The posting period and the level of detail per entry are defined at the start of the project.
Technical discovery call
Leave your details and pick a day that suits you; we will come back to confirm. On the call we listen to your current system, the bottleneck and your goal. There is no charge for the first call.
Your request has been received.